Insurance agencies: IT support for independent agencies
Your clients trust you with their homes, their businesses and their families' details. Your agency has a team that knows your carriers, your systems and your season.
Already have an IT person? Keep them as the first call; we carry security, backups, nights and vacations. How we work with your IT person →
- $155
- per person, per month: Complete with Security + Compliance, which has a $750 monthly minimum.
- Required
- in our plan for every agency that holds clients' financial or health information under the Gramm-Leach-Bliley Act (GLBA).
- Evidence
- built every day as your people train and sign, and kept for the day a carrier asks.
★★★★★ 5.0 on Google · SOC 2 Type II · Founded in Florida in 1995
Thirty minutes with Pedro, Bill or Leah, no pitch. 10 people with Security + Compliance: $2,370 a month with Microsoft licenses. Work out your own number →
IT support for insurance agencies and independent agents in Winter Haven, Orlando, Tampa, St. Petersburg, and Miami.
What the day is like
When a storm is coming, the phones are about to ring. Your office is ready to answer from anywhere.
Before a storm
Ready to work from anywhere
Files and email live in Microsoft 365 and are backed up, so your people can serve clients from wherever the power is on.
When a payment changes
A second look
A request to change where a premium or a refund goes is the oldest trick there is. Multifactor sign-in, email protection and a call-back rule your team agrees make it hard to pull off.
When someone leaves
Access closed the same day
A producer who leaves is removed from email, files and the agency system the day they go, and their license comes off the invoice.
A carrier questionnaire or an insurance renewal due, and nothing to show for it yet? Someone wants proof.
Does one person hold every password? Your IT person is leaving.
Your plan
Complete with Security + Compliance. Clients' financial and health information labeled and protected, multifactor sign-in for everyone, and encryption on every laptop and phone that holds agency data. Encrypted email for applications, loss runs, driver's license copies and anything with a Social Security number in it. Records are labeled and kept as long as your rules require, then deleted after a review, and client details are stopped from leaving by email, chat, a USB drive or an upload. We help your team agree a simple rule: a change to where a premium or a refund goes is confirmed by phone, on a number you already have. Complete is $125 per person, per month, with Security + Compliance at $30 per person on top; Microsoft 365 Business Premium ($22) and the Defender and Purview Suites ($15) are at Microsoft's price. For a 10-person agency that is $2,000 a month for the plan, with Security + Compliance's $750 monthly minimum, and $370 for the licenses, $2,370 in all; the pricing page has every line.
When someone asks for the proof
The Gramm-Leach-Bliley Act (GLBA) treats an insurance agency as a financial institution, and in Florida the insurance privacy rules carry it out: each licensee keeps a written information security program, sized to the agency, with administrative, technical and physical safeguards. The people who ask to see it are usually your carriers first. A Florida carrier's agency agreement, for one, asks for a written information security program, notice of a security incident within 48 hours, and a yearly security questionnaire. Your cyber and errors and omissions (E&O) insurer asks at the application and again at a claim. After a breach, the Florida Attorney General and the Department of Financial Services (DFS) may ask what was in place. With Security + Compliance the program is current, the questionnaire is answered from evidence rather than memory, multifactor sign-in and encryption are on for everyone, and the record of who opened what is kept for a year.
Why it matters
What the proof is worth.
Carriers send the questionnaire first
Your carriers ask for the written program, a 48-hour incident notice and a yearly questionnaire. With Security + Compliance the answers come from the record, not from memory.
Florida asks for a written program
Florida’s insurance privacy rules ask every agency for a written information security program, sized to the agency. We keep yours current with you.
The insurance claim
The application you signed is a promise. After an incident, the insurer asks for evidence that the controls were running. A year of records is where that evidence comes from.
Peace of mind
The day an auditor, an insurer or a large client asks, the answer is already on file. Nothing is assembled the week before, and nothing depends on one person remembering.
Your assessment, in Microsoft’s Compliance Manager
Your rule, scored against your own Microsoft 365.
With Security + Compliance, we set up your rule’s assessment in Microsoft Purview Compliance Manager, which comes with your Microsoft 365. It lists every control the rule asks for, shows what Microsoft has tested for its own cloud, and tracks the rest with us until it is done and on record.
- Access controlPassed
- Audit recordsPassed
- EncryptionPassed
- Risk analysisIn progress
- Workforce trainingPassed
Your three rule templates
Insurance agencies
Your three are chosen from Microsoft’s list of more than 360; a fourth or more is quoted at Microsoft’s price. Microsoft’s score shows progress, not a verdict; the rule’s responsibility stays with your business, and we carry our share of the work.
Complete protects. Security + Compliance proves.
Your plan: Complete, with Security + Compliance.
Everything in Complete stays. Security + Compliance adds four things, for everyone on your plan, at $30 more per person, plus Microsoft’s suites at Microsoft’s price.
| Complete$125 per person | With Security + Compliance+$30 per person, for everyone | |
|---|---|---|
| Deeper protectionMicrosoft’s security and compliance suites, set up and run by your team. | ||
| Sign-ins | Multifactor sign-in, with rules by device and location | Plus risky sign-ins stopped or challenged, even with the right password: a leaked password, an anonymous network, a guessing attack |
| Admin rights | Kept to the people who need them | Given only when needed, for a set time, and taken away after |
| Sensitive information | Labels your people apply; email with sensitive details encrypted or stopped | Found and labeled automatically, and stopped from leaving by a Teams chat, a USB drive or an upload |
| Someone quietly taking data | – | An early warning, and tighter controls for that person |
| An investigation months later | What the security center needs to act today | Six months of every computer’s history, searchable |
| Email attacks | A bad email pulled from every mailbox at once | Plus a campaign seen as one attack, traced and cleaned up across every mailbox |
| Microsoft reaching your data | Microsoft’s standard controls | Only with your approval |
| The proof, kept currentWhat an auditor, an insurer or a partner asks for, already on file. | ||
| Who did what in Microsoft 365 | Kept 180 days | Kept one year |
| Records | Email archived and kept | Email, files and chats kept as long as your rule says, locked when they must not change, then deleted after a review |
| Legal hold | Email, files and chats, with a case and a review | |
| Your rule’s assessment | The baseline assessment Microsoft gives every tenant | Your rule’s own assessment in Microsoft Compliance Manager, with three rule templates chosen with you; Microsoft’s share tested by Microsoft, ours tracked with evidence |
| An evidence report | – | For any audit period, when you or your auditor asks: training finished, practice phishing, policies signed, sign-ins |
| Your map | – | Where your sensitive information lives and who is responsible for each part, written with you and refreshed every year |
| An outside scan | – | What faces the internet scanned from outside every quarter; a penetration test by an independent firm is quoted |
| Your program, kept upThe work people do, so the rules never pile up. | ||
| Policies | – | A policy set from our templates, fitted to your business, reviewed with you every year, and signed by your people |
| Who can reach what | Changed when people join and leave | Plus accounts and settings reviewed as Microsoft changes its systems, and you kept current on what changed and why it matters |
| Training | Short, regular security training with practice phishing | Plus your rule assigned to your training: the courses, the practice phishing and the policy sign-offs mapped to it, and the evidence built as your people finish |
| When a rule changes | – | We tell you what changed and what it means for you, and what we changed |
| Your risk analysis | – | Done with you every year, the first one at setup, and kept on file |
| A security review | Quarterly planning with your team | Plus a security review every quarter: a one-page scorecard of your rule, what we fixed and what we recommend |
| Once a year | Planning for next year | Plus a compliance review: what your rule asks, what we run, and what is still yours to do, and an incident exercise with your team |
| When someone asks, or something goes wrong | ||
| Your insurance application | True answers about the controls we run; you sign | Plus the underwriter’s calls, the extra forms, and the evidence if you ever file a claim |
| A client’s security questionnaire | – | Answered from your record as a draft, with one review call; an audit with live sessions is quoted first |
| An auditor, a regulator or a partner | – | We answer the technical questions with you, from the records and timelines in our systems |
| Your auditor | – | Read-only access to your assessment alone, and one spreadsheet of every control with its status, test date and result |
| A security incident | You hear from us fast, and it is fixed | Plus your insurer’s claims line called first, the logs pulled, the timeline built with you, and the decision you make about who must be told recorded. That decision stays yours, with your attorney |
Part of your plan when you hold
- Patient information, under the Health Insurance Portability and Accountability Act (HIPAA), with our business associate agreement (BAA)
- Clients’ financial information, under the Gramm-Leach-Bliley Act (GLBA): CPA firms, tax preparers and lenders under the Federal Trade Commission (FTC) Safeguards Rule, investment advisers under the Securities and Exchange Commission’s (SEC) Regulation S-P, insurance agencies under Florida’s insurance rules
- Criminal justice information, under the FBI’s Criminal Justice Information Services (CJIS) Security Policy
- Defense contracts, under the Cybersecurity Maturity Model Certification (CMMC)
The rules ask for the written proof, not only the protection.
Recommended in writing when
- An insurer asking for more than the application
- A client’s or a partner’s security questionnaire
- Card payments, under the card industry’s standard (PCI DSS)
- Personal information, under the Florida Information Protection Act (FIPA)
For these, the choice is yours. Answering your cyber insurance application truthfully is in every plan.
Quoted separately: a second rule kept as a full program, another office or site, an audit with live sessions or site visits, a penetration test by an independent firm, a written information security program (WISP) written from scratch, data kept in another region, readiness for a CMMC Level 2 assessment, and acting as your FTC Qualified Individual.
Under the proof, everything in Complete
Your team and everything we do, in the $125.
Who you will know by name
Florida businesses have trusted us since 1995.
We know what it is like when the one person who knows your IT is out. So you get a team, and you know every one of them.
Amazing company! Would highly recommend.
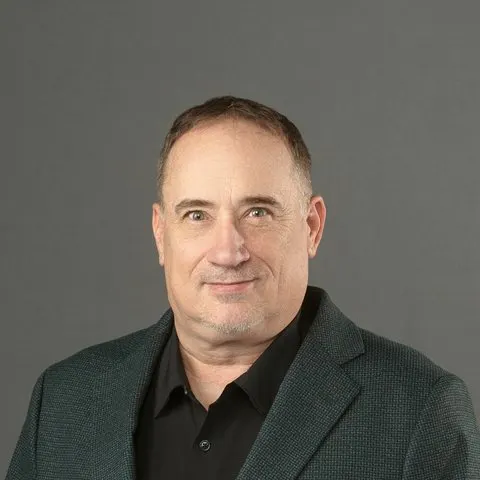
Chris Bridges
Concierge Lead
I keep your business running so you never have to think about technology.
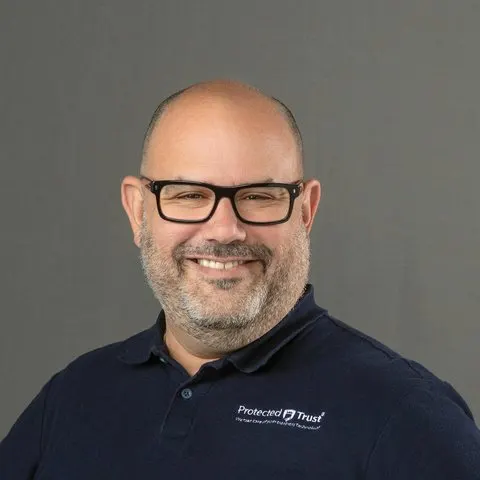
Javier Pereira
Concierge Lead
I take on the projects and the stubborn problems, and explain them in plain English.
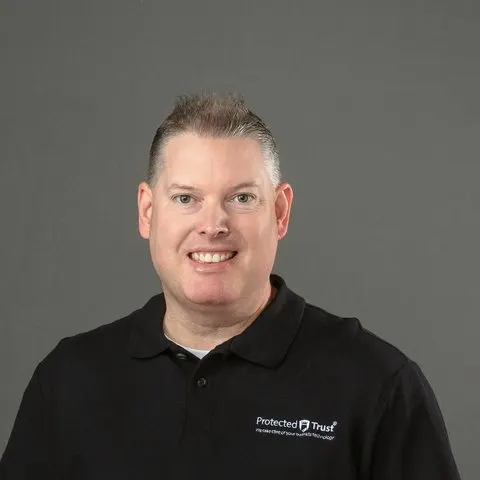
Jonathan Jones
Concierge Specialist
I handle the big moves: migrations, mergers, new devices, and everything Microsoft 365.
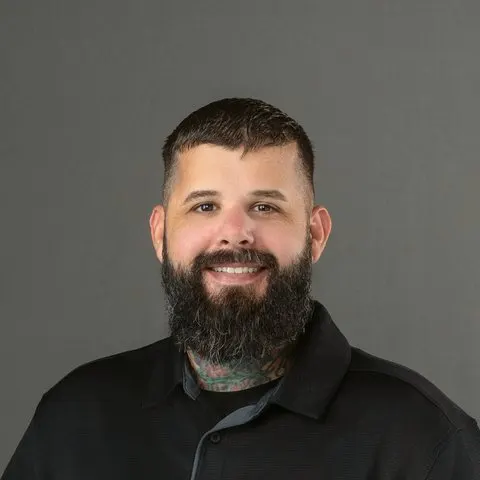
Chris Munoz
Service Engineer, on site
I set up new machines, sort out the network, and come on site when it needs a person.
Your team, from the first call. This is who you will know by name: Chris Bridges and Javier Pereira as your Concierge Leads, with Jonathan Jones and Chris Munoz, the people who know your setup. The whole company is behind them.
Clients join us, and they stay. Our longest relationships go back more than twenty years.
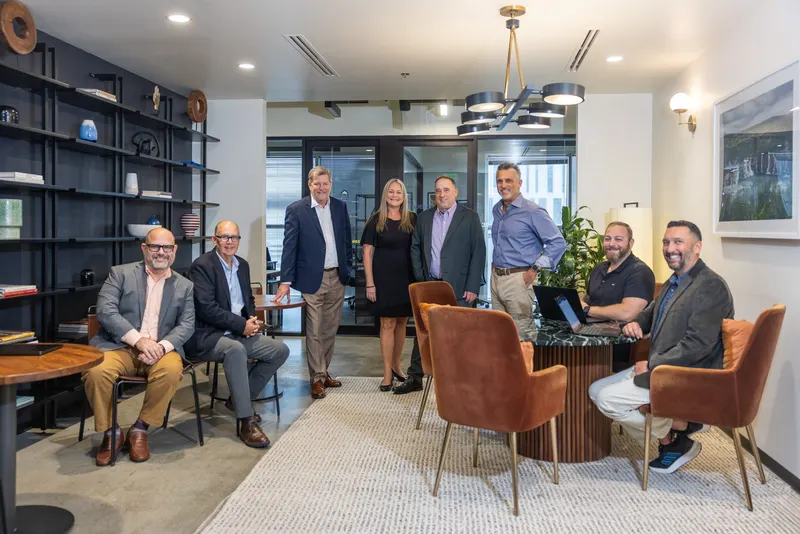
And the whole company behind them.
Your leads know your setup. When something needs more hands, the rest of the company is right there, and every person on our side is named on the team page, with the year they joined.
Meet everyone →How it works
Three steps, and the team is yours.
A 30-minute call
Tell us what is working and what is not. We will tell you honestly if we fit.
Your first month
Day one, you meet your team by name. Most offices are set up within a few weeks; larger ones within 30 days.
Your team takes it from here
You reach out, and someone who knows you takes it on, usually within 15 minutes.
Your plan
Complete, with Security + Compliance.
$125 for Complete plus $30 for Security + Compliance, per person, per month.
For clients' financial and health information
Complete + Security + Compliance
$155per person, per month
Everyone starts here
Complete
$125per person, per month
Your own IT team, security in every plan, Microsoft licenses as their own lines.
For the people who use it
Copilot, AI for work
+$30per person, per month
Microsoft Copilot set up safely, only for the people who need it.
Not ready to talk yet?
Your insurer's renewal questionnaire, answered.
The ten questions carriers ask most, in plain language, why each one is on the form, and one page to score yourself honestly.
Leah writes to you once, by name. Nobody adds you to a list.
Questions people ask
Plain answers.
Do we need Security + Compliance?
Yes, if your agency holds clients' financial or health information, which almost every agency does. Florida's insurance privacy rules ask for a written information security program, and your carriers ask to see it, so Security + Compliance is part of your plan. Answering your cyber insurance application truthfully is in every plan.
What does IT support for an insurance agency cost?
$125 per person, per month for Complete, with Security + Compliance at $30 per person, so $155. Microsoft 365 Business Premium and the Defender and Purview Suites are $37 per person at Microsoft's price. Security + Compliance has a $750 monthly minimum, so a 10-person agency comes to $2,370 a month; the pricing page has every line.
Is our agency under the FTC Safeguards Rule?
No. Under GLBA, an insurance agency answers to its state insurance regulator, not the Federal Trade Commission. In Florida that means the insurance privacy rules and the Department of Financial Services, which licenses agents and agencies.
Can you help us answer a carrier's security questionnaire?
Yes. With Security + Compliance we fill it in with you, from the controls that are actually running, and keep the evidence on file for next year's.
Do you write our written information security program?
We help you write it from our template, fitted to your agency, and make it true. The safeguards it describes are already running, so the program describes what is in place rather than what you hope to do. You stay in charge of it.
If something happens, how fast do we know?
We tell you promptly. Some carriers ask to hear about a security incident within 48 hours, and Florida law gives the agency 30 days to tell affected clients, so tell us your carriers' terms when you start. Your insurer's claims line is called first, and with Security + Compliance we help you write the notices and keep the record.
How do you stop a fake payment request?
Multifactor sign-in on every mailbox, email protection that flags lookalike senders, and a simple rule your team agrees on: a change to where money goes is confirmed by phone, on a number you already have.
Do you work with our agency management system and carrier portals?
Yes. Your team learns the systems your agency runs, keeps the computers, sign-ins and connections around them working, and works with the software company or the carrier when the problem is on their side.
Everything we do, in one place.
Managed IT
Cybersecurity
Industries Medical practices, Law firms, Accounting firms, Financial services, Professional services, Construction, Government, Real estate.
Thirty minutes, no pitch.
With Pedro, Bill or Leah, who look after new clients. You leave with a plan, and you meet your own team before you decide.
Pedro, Bill and Leah
Pick a time to talk- ✓ Help in about 15 minutes, from people who know your setup.
- ✓ Your written information security program, from our template, kept current with you.
- ✓ Policies, training and a year of records, ready for a carrier, your insurer or the state.
- ✓ 10 people: $2,000 a month, plus $370 in Microsoft licenses and security suites: $2,370 a month.
“Every one of their techs that I've worked with have been professional, quick to respond and don't just fix the issue, but educate me on what was done and recommendations for any related issues. Personal, professional, reliable!”